US Seizes Domains Tied to Alleged Chinese Hacking Tools Targeting Federal Agencies
The DOJ and FBI say they disrupted state-backed tools, QScan and QTRouter, used to breach agencies including NASA, the Federal Reserve and the Senate.

AfroEuropa Newsroom
AfroEuropa desk
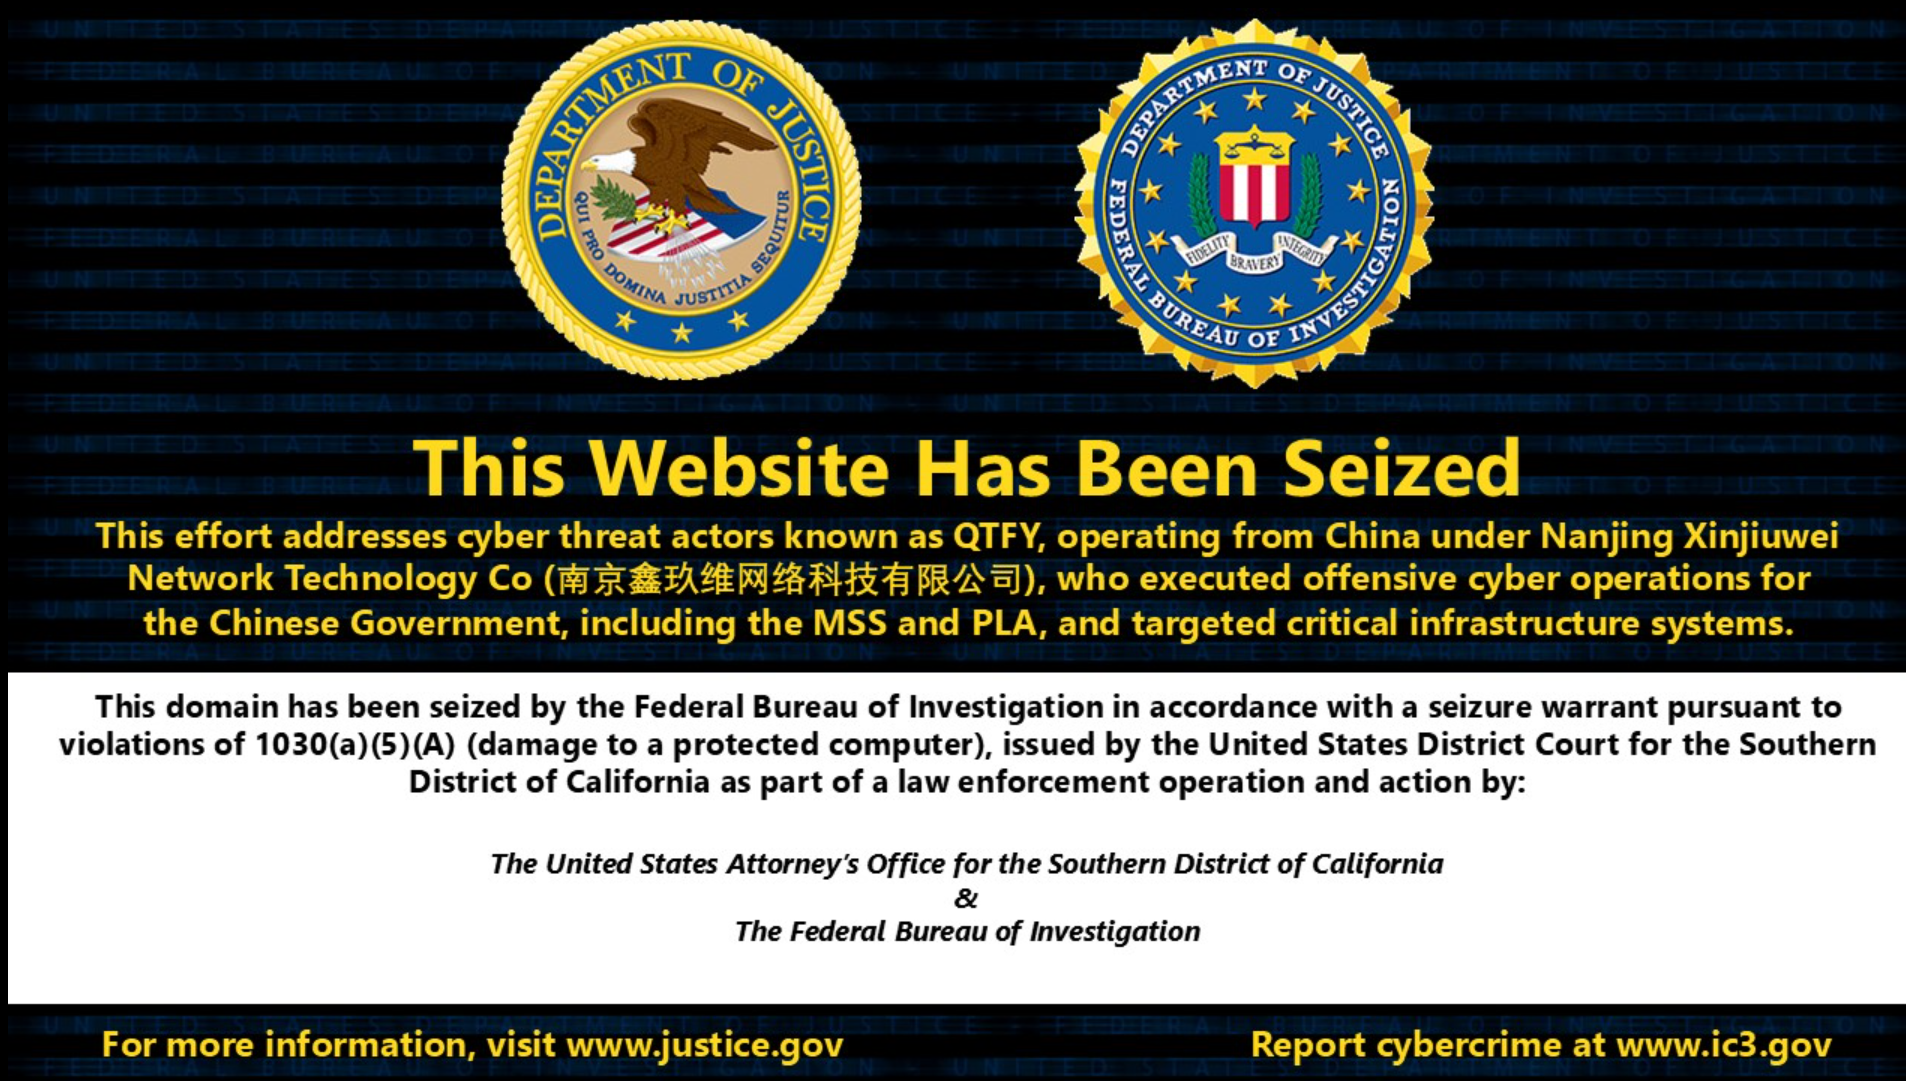
The U.S. Department of Justice and the FBI said they seized internet domains linked to hacking tools that the government attributes to a China state-sponsored group. The action, announced in a statement on Wednesday, targeted infrastructure the DOJ says was used to scan, infect and exploit Internet of Things (IoT) devices in attacks on federal agencies and multiple industries.
According to the DOJ, a group identified as QTFY was responsible for the activity, which relied on two pieces of malware called QScan and QTRouter. As reported by Tom's Hardware, the government says QScan scans and automatically infects thousands of IoT devices worldwide, which are then folded into the QTRouter network. The DOJ described that network as a botnet that also functioned as an obfuscation layer to hide the source of malicious traffic.
Keep reading
Anthropic Says Russia- and China-Linked Actors Used Claude in Espionage and Weapons Work
The AI company reports it detected and disrupted state-linked groups using its Claude models for hacking campaigns and military development projects.
Other highlights
Google's Motion Assist Feature Expands Beyond Pixel to More Android Devices
Google is rolling out Motion Assist, a tool meant to ease motion sickness, to a wider range of Android phones running Android 17 or higher.
Follow the story
One newsletter, two continents
The Bridge brings you the tech, startups, and leaders moving between Africa and Europe in one sharp email each morning. No spam, unsubscribe anytime.